Anti-Spoofing
A GPS spoofing attack attempts to "deceive" a GPS receiver by broadcasting counterfeit GPS signals, structured to resemble a set of normal GPS signals, or by rebroadcasting genuine signals captured elsewhere or at a different time. These spoofed signals may be modified in such a way as to cause the receiver to estimate its position to be somewhere other than where it actually is, or to be located where it is but at a different time, as determined by the attacker.
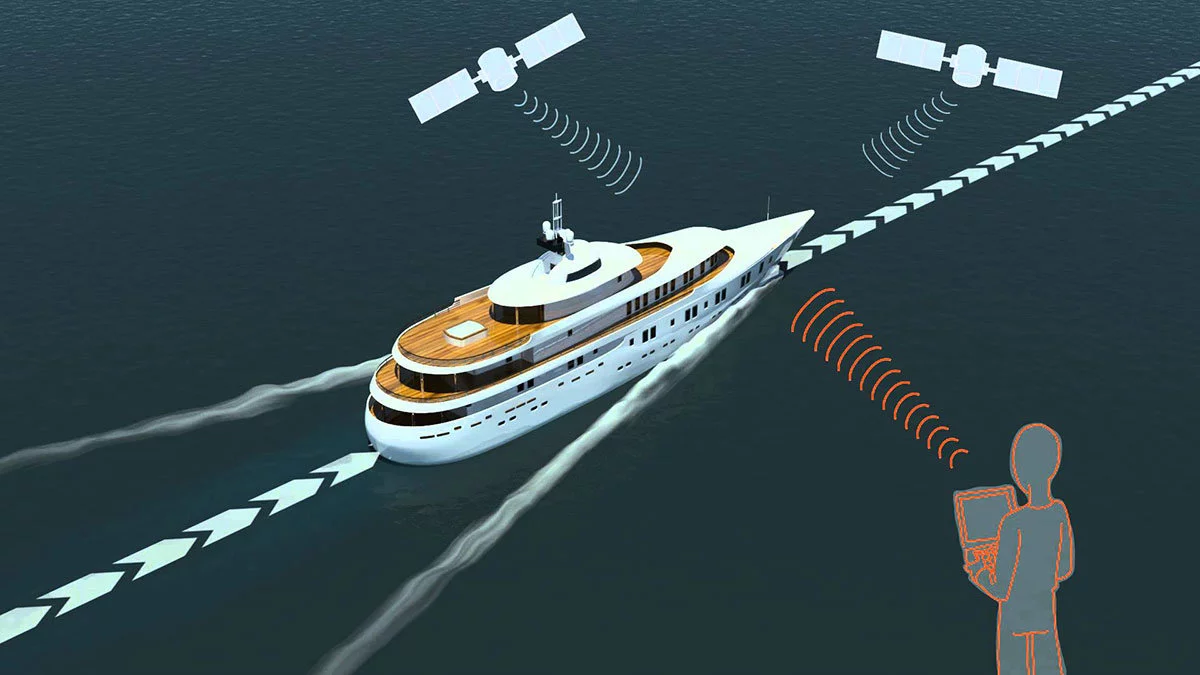
Spoofing attacks have become increasingly common since 2023. One of the earliest suspected cases was the capture of a Lockheed RQ-170 drone aircraft in northeastern Iran in December 2011, that likely was the result of such an attack. Currently, multiple spoofing events are detected daily using ADS-B reports from aircraft.
For a number of years, Stanford has been performing research on how to make GPS and GPS receivers more robust against spoofing attacks. Current research includes the following techniques:
- Using WAAS message authentication
- Time of arrival techniques
- Use of antenna to distinguish direction of arrival
- Using and comparing encrypted P(Y) code
The FAA has supported Stanford's research in this area.
For More Information
- View Inside GNSS article (PDF): A Multi-Antenna Defense: Receiver-Autonomous GPS Spoofing Detection , by Paul Montgomery (Novariant, Inc.), Todd Humphreys (University of Texas at Austin), and Brent Ledvina (Virginia Tech), March/April 2009.